CA-to-CA Migration
Move every endpoint. Prove every move.
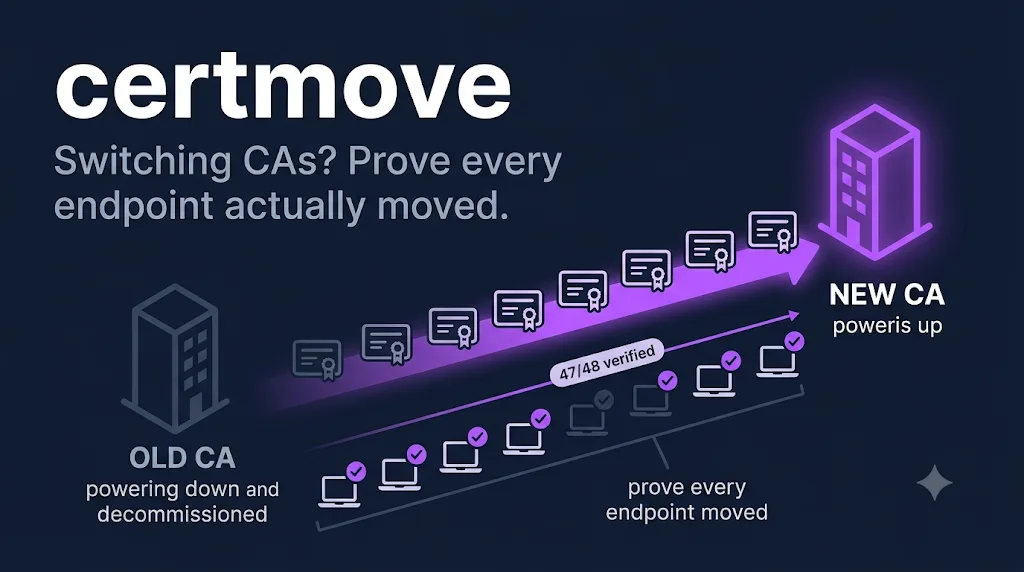
Why this tool exists
Switching CAs sounds like a procurement decision. In practice it is a months-long migration that the auditor will eventually ask you to prove — every endpoint, every replacement, every old certificate retired.
certmove plans the migration from a source inventory, tracks replacement as it happens, and writes a tamper-evident evidence log the auditor can verify against the live endpoints.
The PASS/FAIL evidence row is the differentiator. It is the artifact that turns "we believe we migrated" into "here is the proof, signed and timestamped".
What it does
01Plan the migration
python3 certmove.py plan --inventory source_inventory.csv --from-ca Entrust --to-ca Sectigo --out migration_plan.csvFilters source inventory to certificates issued by the outgoing CA and writes a per-endpoint migration plan with target dates and ownership.
02Verify post-migration
python3 certmove.py verify --inventory post_migration.csvRe-scans each endpoint, checks that the live certificate is now issued by the new CA, and emits a PASS or FAIL per row. PASS rows include the new serial, fingerprint, and timestamp; FAIL rows surface why.
03Generate the evidence log
python3 certmove.py evidence --verify-output verify.json --out evidence_log.csvProduces a sorted, hash-chained CSV with one row per endpoint. Hand this to your auditor; pair it with the source inventory and the new CA's issuance log for a complete trail.
Sample output
Exactly what the tool writes to your terminal. No mockups — this is real output, copied verbatim.
$ python3 certmove.py verify --inventory post_migration.csv

[ MIGRATION VERIFICATION — Entrust -> Sectigo ]

  api.example.com:443        PASS  issuer=Sectigo  serial=0x9c:a1:...  not_after=2027-04-11
  www.example.com:443        PASS  issuer=Sectigo  serial=0x9c:a2:...  not_after=2027-04-11
  legacy.example.com:443     FAIL  issuer=Entrust  -- still on old CA, not replaced
  vpn.example.com:443        PASS  issuer=Sectigo  serial=0x9c:a3:...  not_after=2027-04-11

  Summary: 3 PASS, 1 FAIL, 0 unreachable.
  Evidence log written: evidence_log.csv  (sha256: 4a7b2c...)

  -> 1 endpoint still on the old CA. Drive that to zero before retiring trust.
Common questions
Get the tool
GitHub
Clone the repo, install one dependency, run the tool.
git clone https://github.com/patjenkinsGIT/cert-automation-toolkit.git
cd cert-automation-toolkit
pip install cryptographyDirect download
Grab the latest release zip — everything in one file.
Download v1.0.0.zipMIT-licensed. No setup notes beyond the README in the folder.