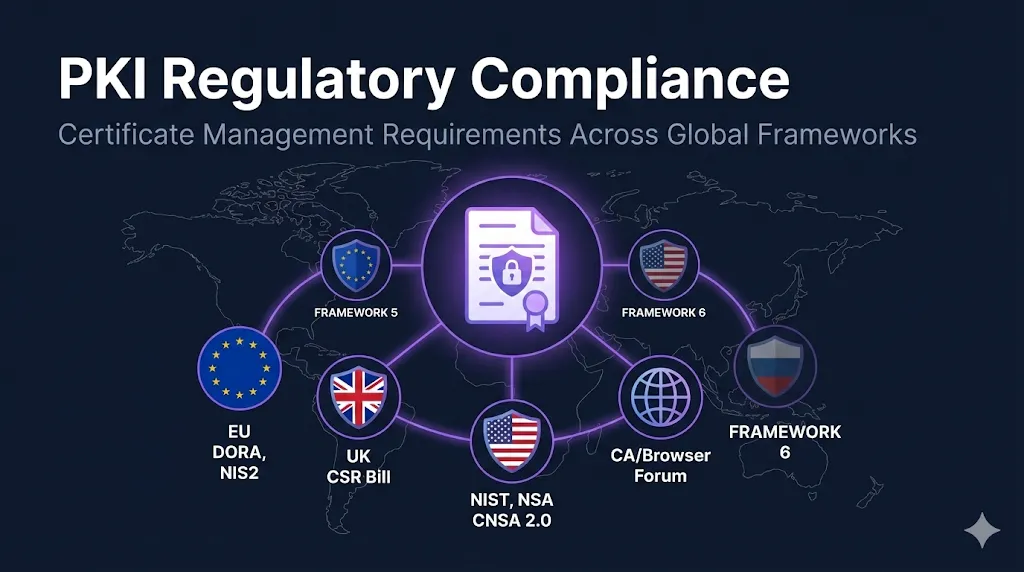
EU Regulations
DORA, NIS2
US Standards
NIST SP 800-57/52, NSA CNSA 2.0
UK Legislation
CSR Bill
Industry Standards
CA/Browser Forum

Why This Series Matters
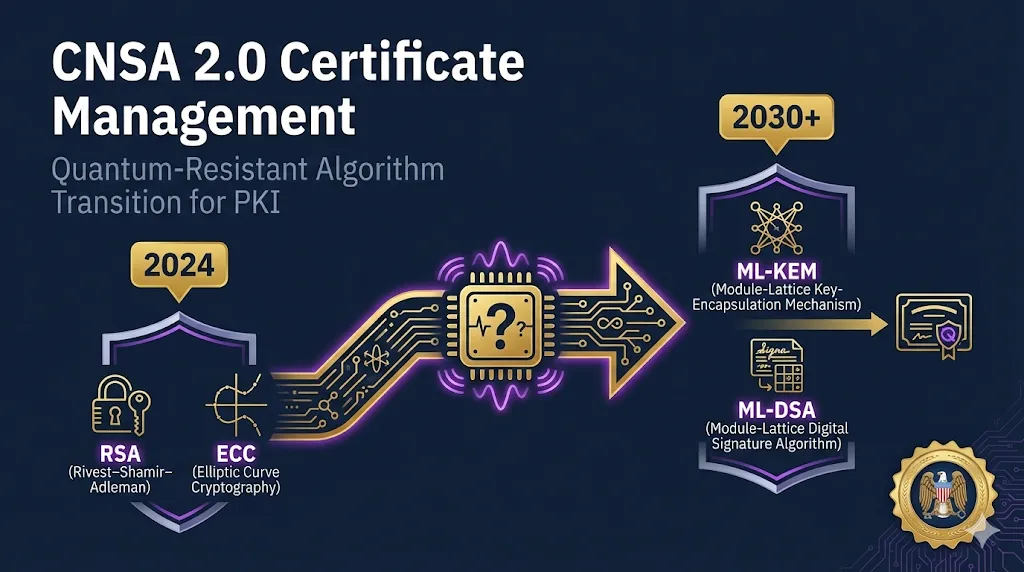
Compliance frameworks increasingly recognize cryptography and certificate management as critical controls. Whether you're preparing for DORA's January 2025 enforcement, aligning with NIS2's Article 21 requirements, or planning your CNSA 2.0 post-quantum transition, these guides translate regulatory language into actionable CLM controls.
Each guide includes:
- • Requirement-to-CLM control mapping tables
- • Implementation checklists with timelines
- • Auditor evidence guidance
- • Cross-references to related FixMyCert resources
Related Resources
PKI Maturity Assessment
Score your certificate management maturity across 6 categories and get prioritized recommendations.
Post-Quantum Cryptography Guide
Understand ML-KEM, ML-DSA, and what your PKI team needs to do before 2035.
Checklists & Runbooks
Actionable procedures for certificate operations, incident response, and compliance audits.