Back to Demos
31/54
What is HSTS?
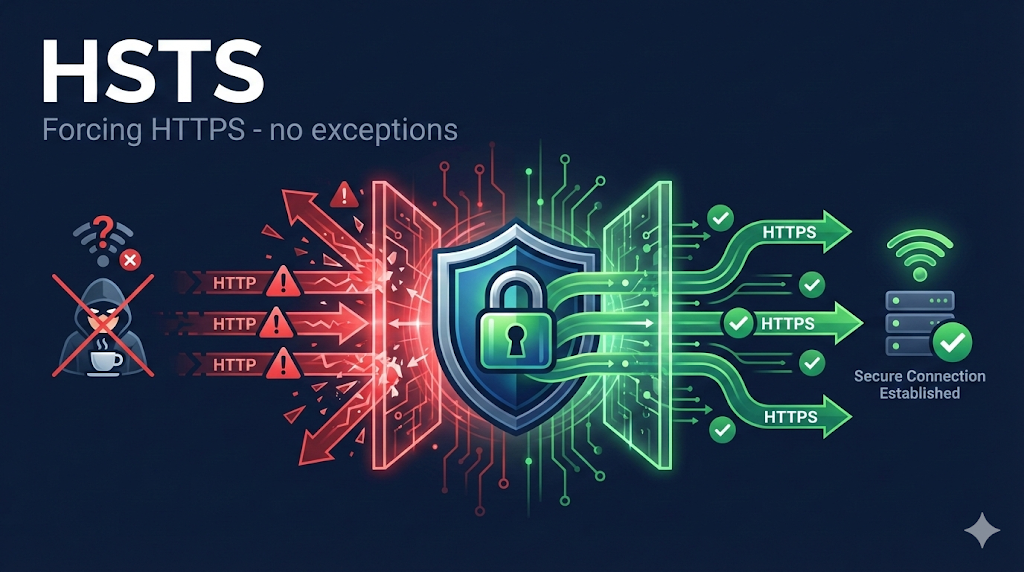
HTTP Strict Transport Security (HSTS) is a security header that tells browsers to always use HTTPS for your domain. Once enabled, browsers will never attempt an HTTP connection - eliminating the vulnerable redirect that attackers can exploit.
Browser tries
HTTP
Server says
"Use HTTPS!"
Browser caches
HSTS policy
Future visits
HTTPS only
The SSL Stripping Problem
Without HSTS, there's a dangerous moment when you first visit a site:
You type
example.comHTTP request sent!
Server redirects to HTTPS
That initial HTTP request can be intercepted on public WiFi! An attacker can serve a fake HTTP version of the site and steal your credentials. This is called an SSL stripping attack.
How HSTS Fixes This
No HTTP attempts
Browser converts http:// to https:// internally
Cached protection
Policy remembered for months/years
Subdomain protection
Optional includeSubDomains directive
Preload list
Hardcoded in browsers for zero first-visit risk